Canada Shuts Down Government Websites Due to Critical PHP Vulnerability
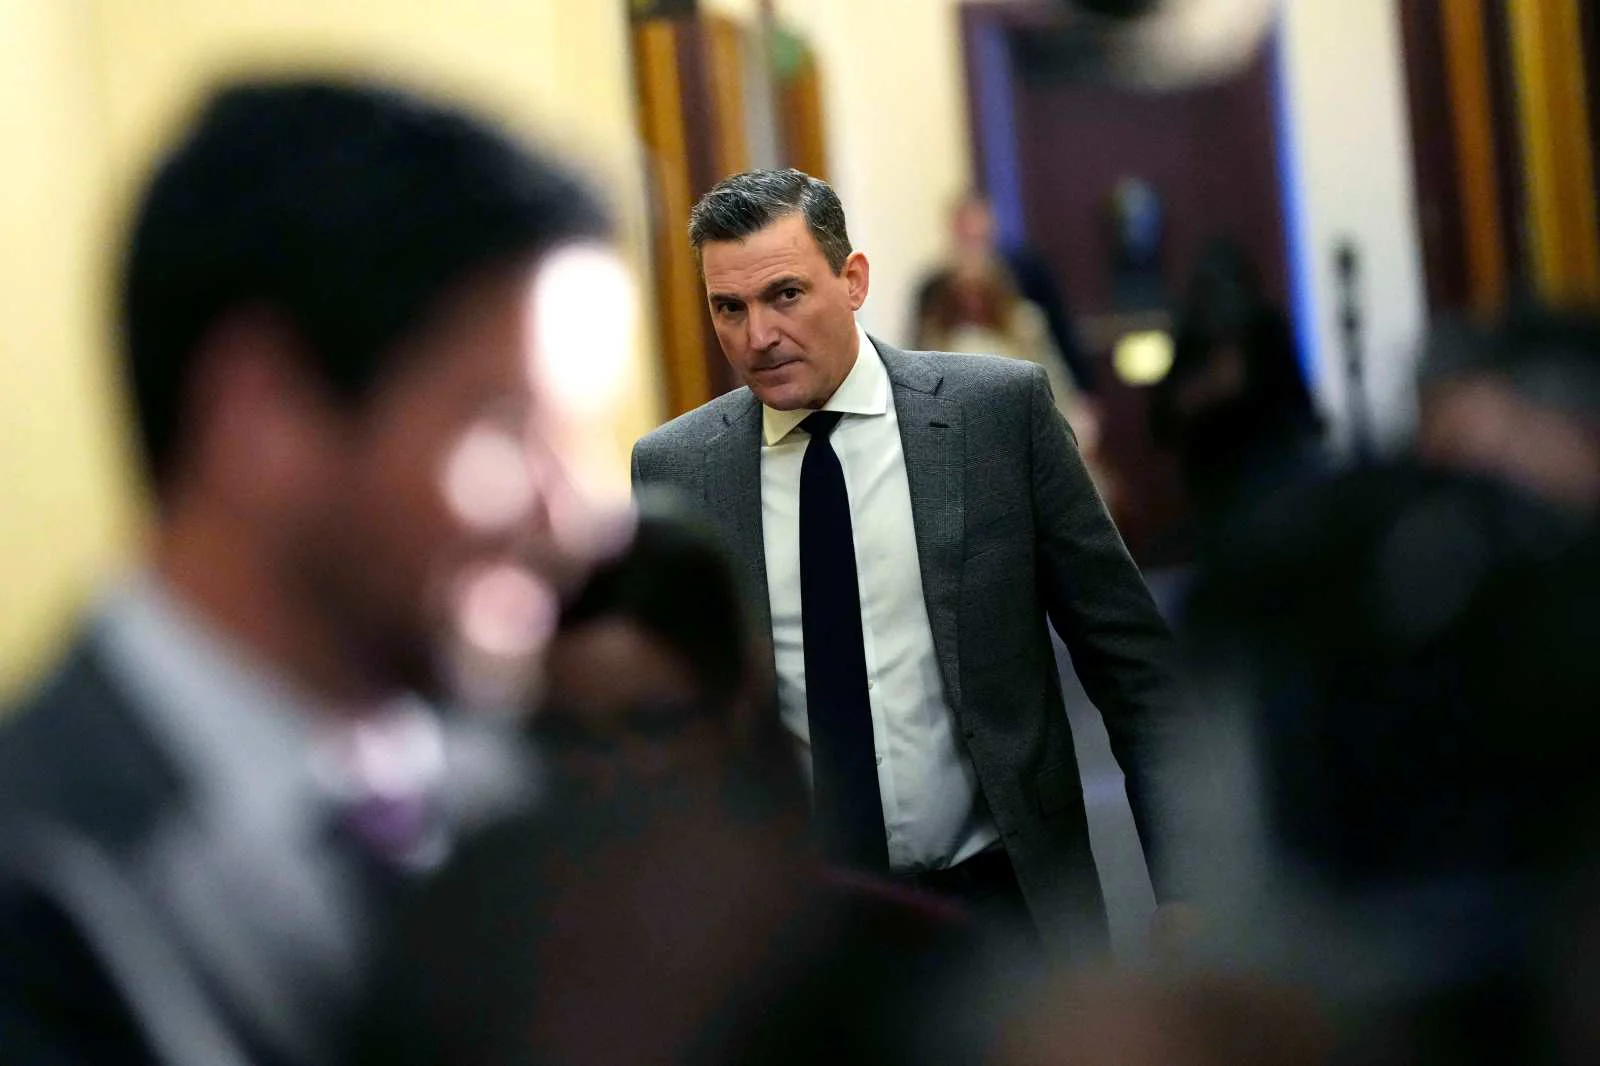
On October 21, 2026, some Canadian federal government websites were temporarily taken offline following warnings about critical vulnerabilities in PHP. Artificial Intelligence and Digital Innovation Minister Evan Solomon confirmed the precautionary action, citing guidance from the Canadian Centre for Cyber Security.
Key Takeaways
- Global Software Footprint: PHP is used by roughly 70% of websites with an identifiable server-side programming language, making vulnerabilities in the software a widespread security concern.
- Proactive Defences Deployed: Government authorities took public portals offline pre-emptively to shield critical databases from unauthenticated remote code execution.
- Specific Vulnerabilities Disclosed: The official advisory documents two distinct technical flaws tracking under identifiers CVE-2026-109618 and CVE-2026-109619.
Systemic PHP Vulnerability Triggers Public Sector Containment
The immediate infrastructure intervention targets critical remote code execution vulnerabilities within web application programming environments. According to reporting by the Global Cyber Defense Monitor, the security risks could allow unauthorized actors to compromise backend state systems without credentials.
The Canadian Centre for Cyber Security has advised organizations to apply available PHP security updates immediately and assess internet-facing systems for potential exposure. Technical teams are validating localized platforms to ensure compliance with the newly released software updates.
Coordinated Regional and International Security Response
According to coverage by Winnipeg Free Press, The response has also affected services beyond federal government websites.
According to coverage by The Ottawa Bureau Report, Newfoundland and Labrador reported temporary provincial website disruptions, while the University of British Columbia warned that some university websites and services might be unavailable as security updates were applied.
The defensive steps taken by Canadian regulators align with international protocols enacted concurrently across Western Europe. Digital service bodies in multiple nations implemented similar operational updates to integrate the code corrections issued on October 21, 2026.
📅 What to Watch Next
Affected government websites are expected to return once the necessary security patches have been applied. Minister Evan Solomon has not provided a confirmed restoration deadline for all affected services.
Key Story Metrics & Analytical Comparison
| Jurisdiction / Node | Operational Action | Stated Administrative Intent | Official Oversight Body |
|---|---|---|---|
| Canadian Federal Portals | Precautionary Offline Containment | Mitigation of Vulnerabilities | Canadian Centre for Cyber Security |
| Newfoundland and Labrador | Temporary Provincial Disruptions | Precautionary Service Suspension | Local Technical Teams |
| University of British Columbia | Precautionary Access Restrictions | Network Update Deployment | University IT Services |
Frequently Asked Questions
Was any citizen data exfiltrated during the infrastructure shutdown?
Canadian authorities declared that no active exploitation had been identified at the time of publication, though official advisories caution that the situation could change. The precautionary service suspensions were enacted as a defensive barrier rather than a response to a confirmed network compromise.
How can third-party website operators resolve this programming language issue?
Independent operators running web applications must immediately apply the official security patches released by the programming foundation to their servers. Organizations should also check for secondary system updates across connected platforms.